Industry news
Regulation, resilience and the practice of getting it right.
Analysis on DORA, NIS2, ISO 27001 and ICT risk for regulated financial institutions in Cyprus and the EU.
Events
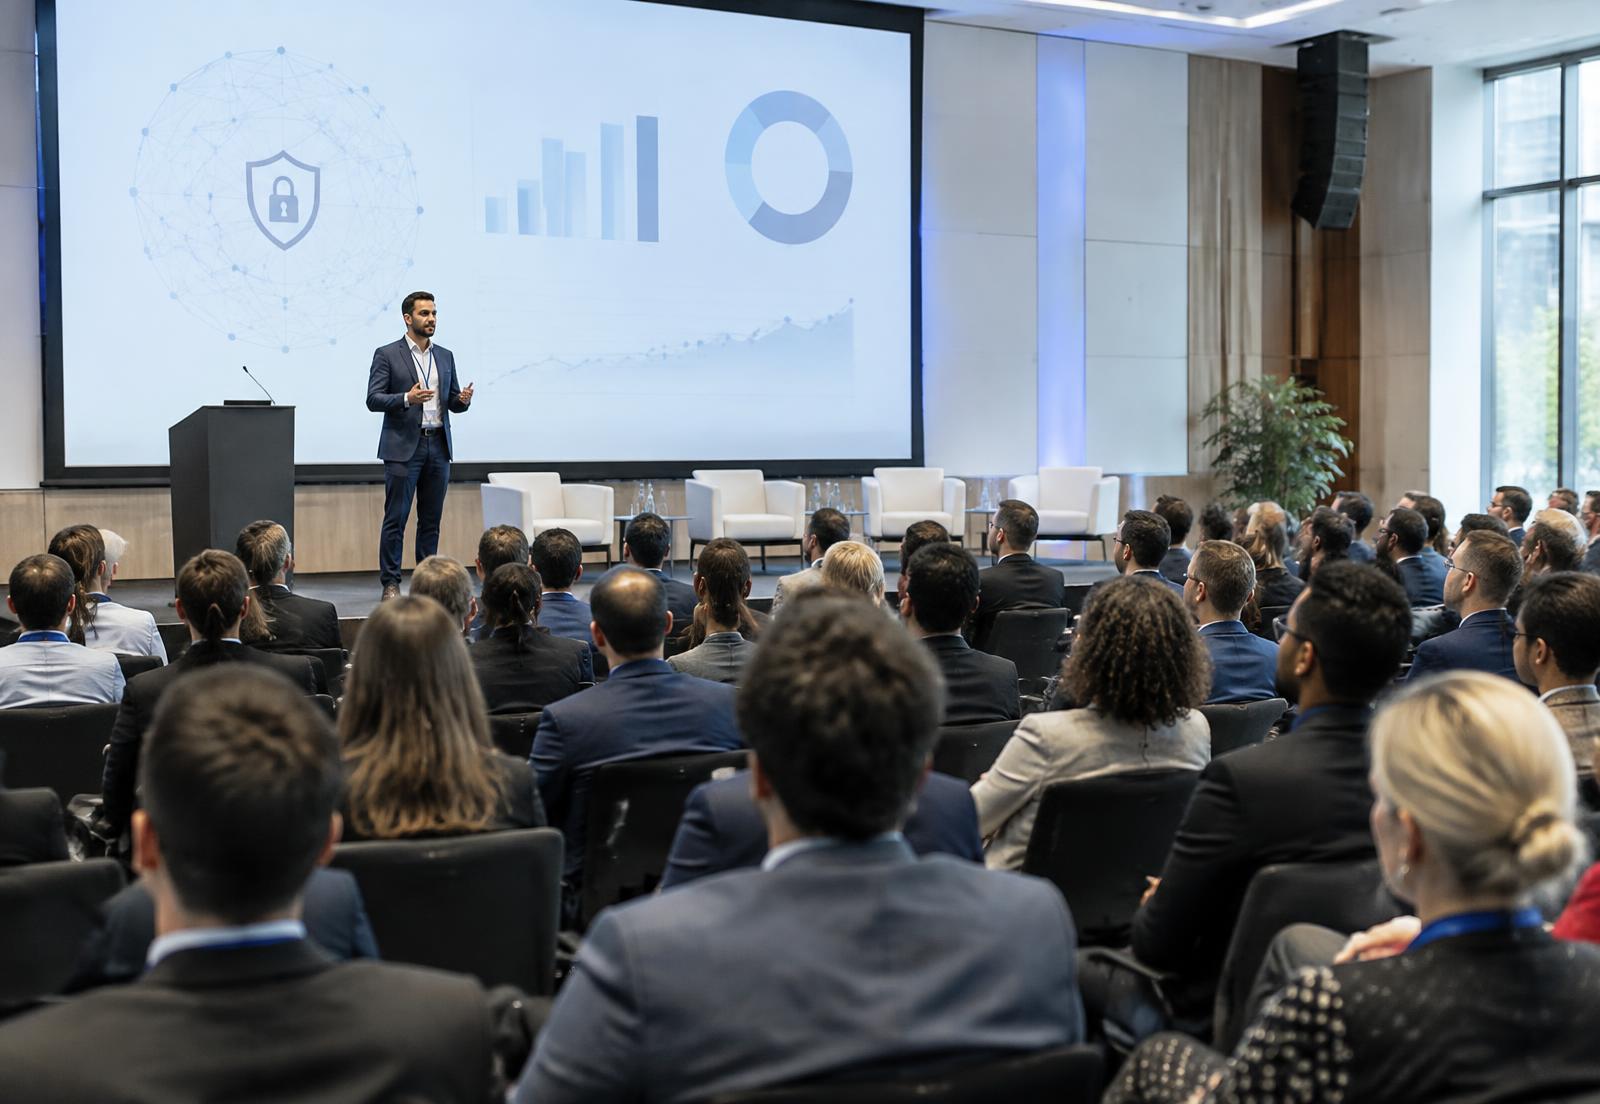
Executive briefing: from regulatory evidence to wallet security
Finalogic, AmagisTech and Crystal Intelligence are bringing senior leaders together in Nicosia for a focused discussion on defensible compliance and digital-asset security.
Read the analysis
Regulation
DORA in its second year: what supervisors are actually testing
The register of information is filed. Now supervisors are asking whether the resilience testing behind it is real.
Governance
NIS2 in Cyprus: who is in scope and what changes at board level
Management bodies now carry direct accountability for cybersecurity risk-management measures — with personal consequences.
Standards
ISO 27001 without the theatre: certifying a system you actually run
A certificate earned through a binder of policies nobody follows is a liability, not an asset.
ICT Risk
Concentration risk: when everyone depends on the same three providers
Outsourcing registers show diversity. Dependency mapping usually shows the opposite.
Emerging Technology
AI governance for regulated firms: start with the inventory
Before you write an AI policy, find out how many models and vendor features are already in production.
Contact
Start a confidential conversation.
Tell us about your regulatory deadline, audit finding or certification target. We respond within one business day with a qualified point of contact.
- Office
- Kafkasou 9, 2112, Aglantzia, Nicosia, Cyprus
- info@finalogic.com